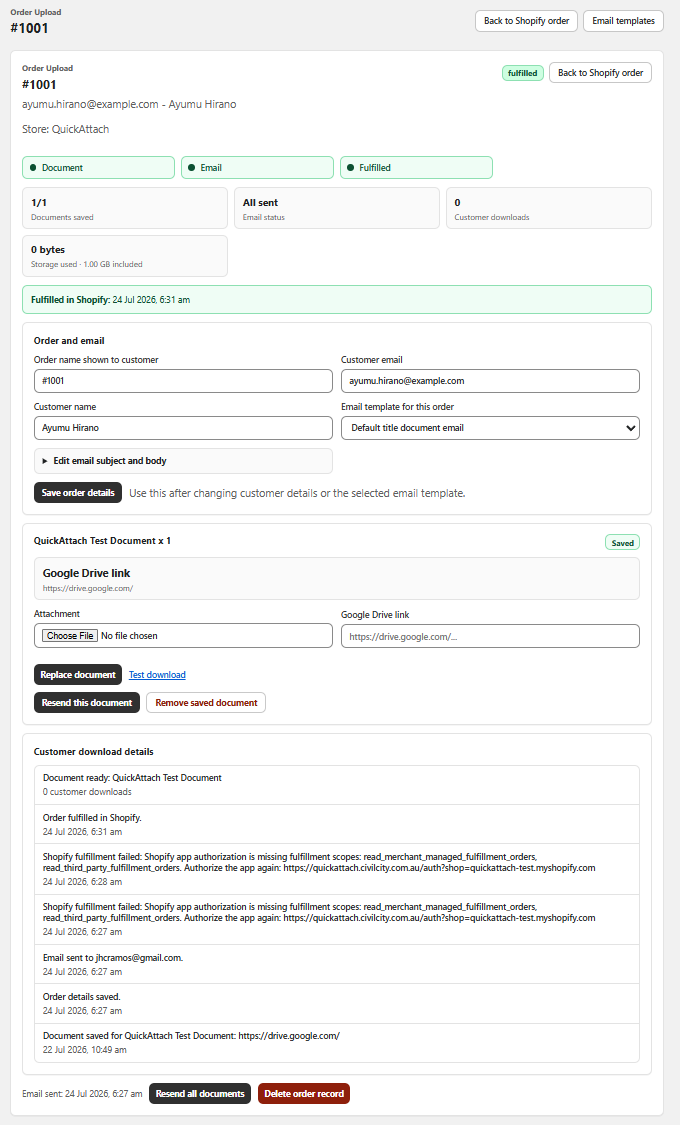
Review the whole delivery path
A document can be correctly attached to an order and still have an inappropriate external sharing setting. It can also have the right permissions but contain another customer’s information. Treat content matching and access control as separate checks.
QuickAttach documents order-specific files and links. This article does not claim a security certification, legal compliance, or immunity from sharing. For sensitive work, evaluate the complete system and the requirements applicable to your business with the appropriate responsible people.
A private-document release checklist
- Contents: open the exact release and confirm it contains only the intended material.
- Identity: match order, item, and recipient using the store’s established verification process.
- Location: confirm the storage system is suitable for the document’s sensitivity.
- Access: test the intended customer route and investigate external permissions separately.
- Exposure: remove unnecessary personal information from filenames and message previews.
- Availability: record the applicable retention or expiry conditions.
- Exceptions: assign a person to access failures, mistaken releases, and deletion questions.
These are operational recommendations, not an assurance that checking seven boxes satisfies every obligation. Avoid testing with real private documents; use synthetic copies that preserve the relevant format without the sensitive content.
Fictional example: a personalized equipment assessment
Order 4601 contains an assessment produced for one customer’s workspace. Before delivery, the reviewer notices that an appendix includes an earlier project’s contact details. They correct the export and review it again. The delivery operator then confirms the order association and tests the recipient path with a harmless sample in the same configured workflow.
The mistake was in the file contents, so a secure-looking link would not have fixed it. Similarly, a correct PDF would not excuse placing it in a public folder.
Avoid public storage by habit
Shopify warns that Content > Files is for public-access material and should not hold confidential, personal, or sensitive information. Do not use that area as a convenient private-document repository.
For an external destination, review the provider’s access settings directly. For app-hosted delivery, ask specific questions about access, deletion, and retention rather than inferring them from the word “secure.”
The QuickAttach support page recommends checking the customer email, download link, and external sharing permissions. Combine those checks with content review and a clear incident process so staff know what to do when a release does not match the intended recipient.
Explore this topic
- Shopify Files vs Private Order Downloads: Where to Store Customer Documents
- A Secure App Link Does Not Fix Public Google Drive Permissions
- File Retention vs Download-Link Expiry: What Merchants Should Know
- What Happens When a Digital Download Link Is Forwarded?
- Remove Personal Information from File Names Before Delivery
- Review Staff Access to Customer Files in a Shopify Store
- Plan Customer File Deletion Across Shopify and External Storage
- Create a Backup Plan for Made-to-Order Digital Deliverables
- What Download Tracking Can and Cannot Prove
Deliver the right file with the right order
See how QuickAttach connects a customer-specific file or link to a Shopify order item.
See the QuickAttach order-to-download walkthrough