The destination keeps its own rules
When a delivery workflow sends a link to an external file, the external provider still decides who can open that destination. Google Drive’s sharing documentation distinguishes restricted access from access for anyone with the link. A separate app link does not rewrite those settings.
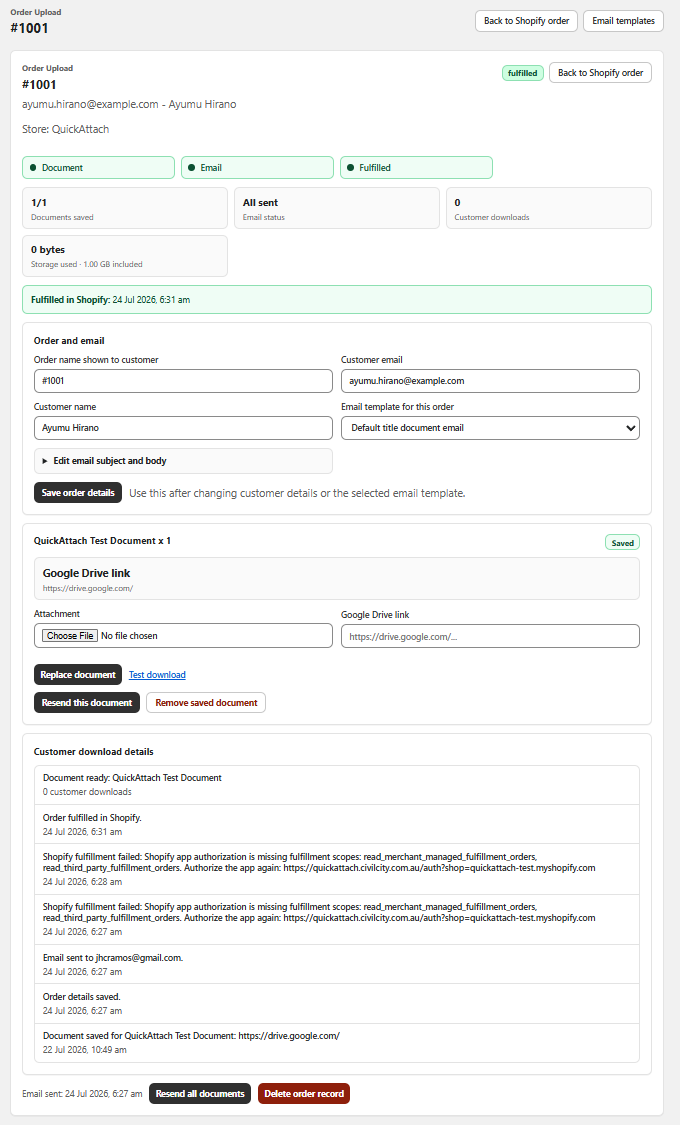
QuickAttach supports external links for order items. That is not the same as copying the file into app storage, taking a backup, or changing Google permissions. Review both parts of the path.
A two-layer access matrix
| App path | External destination | Operational implication |
|---|---|---|
| Works for intended buyer | Correctly restricted | Verify the buyer’s provider identity can open it |
| Works for intended buyer | Broadly shared | Destination exposure remains broader than the order |
| Unavailable | Still accessible directly | Ending the app path does not establish provider revocation |
| Works | Permission denied | The provider access issue still needs resolution |
The matrix describes independent layers. It does not assert a particular authentication mechanism for QuickAttach.
Fictional example: a shared project folder
A merchant delivers order 4603 through a link to a folder containing a custom plan. The folder also contains another synthetic test project and has broader sharing than intended. The merchant creates or selects an appropriately scoped destination, checks its effective permissions, and confirms that only the intended material is present.
Changing the email wording would not correct the folder contents or sharing. Those decisions belong at the provider. Google also documents that folder access can affect the files inside it, so inspect the surrounding location rather than only the individual filename.
A controlled external-link check
- Use a harmless test file and record the intended audience.
- Inspect the provider’s sharing settings and relevant folder context.
- Open the destination as the intended recipient in a separate browser context.
- Check a controlled unauthorized context only with synthetic material.
- Record whether the result matches the intended access design.
- Recheck after moving the file or changing sharing settings.
This is a proposed protocol, not a security audit or completed test. QuickAttach support specifically recommends checking external link permissions. Keep that responsibility assigned to someone who can administer the external destination, and do not treat the delivery app as a substitute for that access review.
Deliver the right file with the right order
See how QuickAttach connects a customer-specific file or link to a Shopify order item.
See the QuickAttach order-to-download walkthrough