Do not infer access control from the shape of the URL
A long or unusual link can still grant access to anyone who possesses it. Another route may require an authorized account. The only useful claim is one supported by the delivery system’s documentation and the behavior you verify in the relevant configuration.
QuickAttach documents file delivery and tracking, not DRM or a guarantee against forwarding. For external destinations, the provider’s sharing rules remain relevant. Google Drive, for example, distinguishes restricted access from anyone-with-link access.
A safe forwarding test setup
- Create a synthetic order and a harmless file with no personal information.
- Use one controlled account as the intended buyer.
- Use a second controlled account or signed-out context as the comparison.
- Record the intended access policy before testing.
- Keep working links out of public reports and screenshots.
Do not forward a real customer’s private link to investigate this question. The test should reveal behavior without creating a new disclosure.
Run and interpret the cases
| Case | Observation to record | Interpretation limit |
|---|---|---|
| Intended buyer opens link | File available or access rejected | One successful route only |
| Controlled other context opens link | File, sign-in, or denial | Behavior of this configured route |
| External destination opened directly | Provider’s effective access | Separate from app-link behavior |
| Buyer saves file locally | A local copy exists | Hosted-link controls do not establish control of that copy |
Fictional example: a public destination behind a delivery link
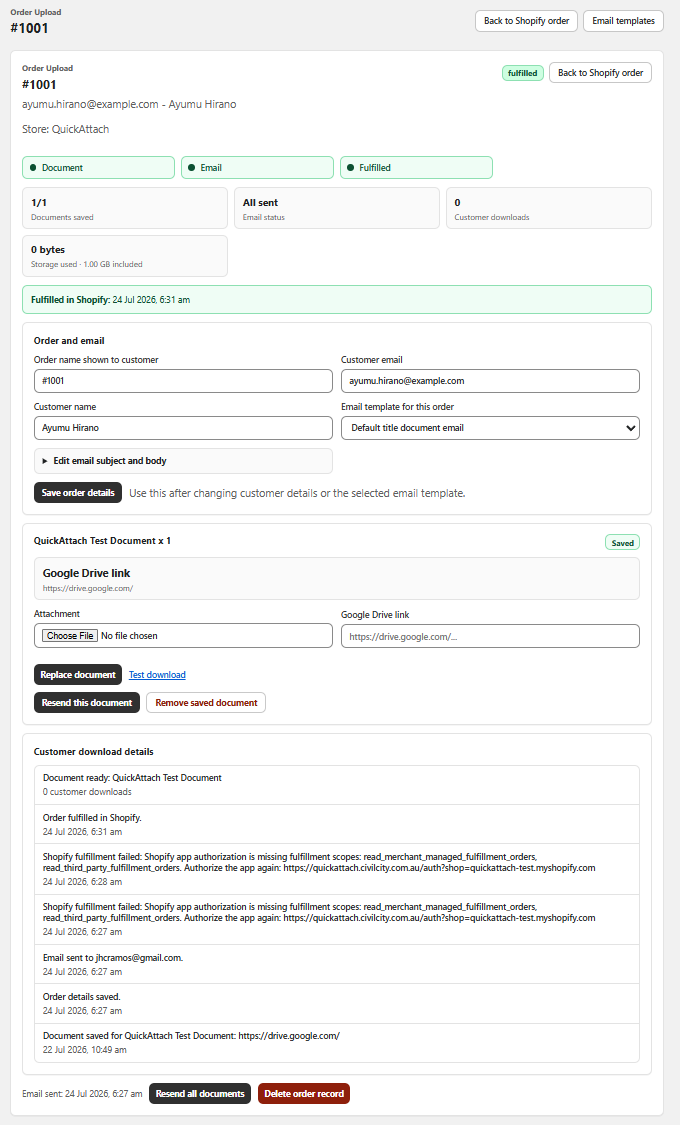
For order 4605’s synthetic report, the merchant finds that the external destination can be opened in a signed-out context. The finding concerns that destination’s permissions. The merchant reviews those settings and customer requirements rather than assuming that the app’s order association prevents direct access.
This is an illustrative scenario, not a completed test or a statement that all QuickAttach links behave the same way.
Write promises within the evidence
Explain the access route you actually provide and the customer’s permitted use through the store’s applicable terms. Avoid “impossible to share” or “only the original buyer can ever see it” unless the full claim can be supported—and remember that a downloaded file is another copy.
Ask support about uncertain app behavior, and record your own test context and limitations. A precise statement about a verified access control is more useful than an absolute security promise.
Deliver the right file with the right order
See how QuickAttach connects a customer-specific file or link to a Shopify order item.
See the QuickAttach order-to-download walkthrough